Topic
Security
5articles about Security.
Well-Known URIs in Production: Deploying security.txt and A2A agent-card.json
Deploy RFC 8615 /.well-known/ endpoints without silent CDN failures. Covers RFC 9116 security.txt, A2A agent-card.json, and MCP routing.
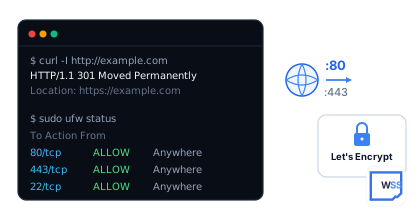
Why Port 80 Is Required for ACME HTTP-01 Renewals: Troubleshooting AWS Ingress and Port 443 Failures
A production debugging runbook for ACME HTTP-01 validation drops, intermediate certificate breaks, ALB redirect loops, and NLB protocol mismatches.
Trusted Types API: Production Deployment
Deploy Trusted Types safely: configure default policies, audit indirect DOM sinks, enforce CSP headers, and integrate Vite or Angular builds.
Content Security Policy (CSP): Architecting Strict CSP with Nonces and Hashes
How to architect a strict CSP that prevents XSS without breaking edge caches or runtime inline scripts — covering hashes vs. nonces tradeoffs.
Subresource Integrity (SRI) in a Dynamically Imported World
Apply CSP and SRI hashes to dynamic import() calls and third-party vendors — covering Import Maps and integrity constraints on dynamic scripts.